

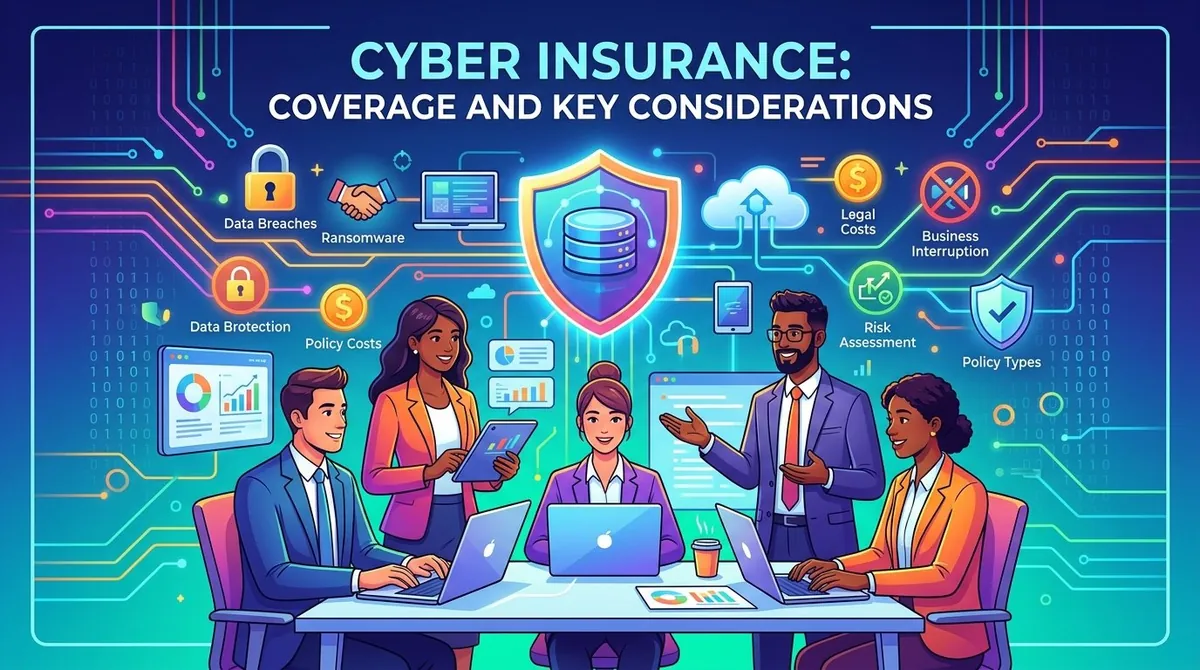
Businesses increasingly rely on digital systems to store information, communicate with customers, process payments, and operate everyday activities. A cyber incident can therefore create costs that extend beyond repairing technology, including business interruption, legal expenses, customer notification, and regulatory obligations.
Cyber insurance is designed to help businesses manage financial risks associated with cyber incidents such as data breaches, ransomware, phishing, and certain network security failures. Coverage varies significantly between policies, and insurers may apply specific limits, exclusions, conditions, and security requirements.
Understanding what cyber insurance can cover and what a policy may exclude is important when evaluating coverage. Businesses should consider their information systems, data, operations, contractual obligations, and existing insurance before selecting a policy.
What Is Cyber Insurance?
Cyber insurance is a type of insurance designed to address financial losses and liabilities associated with cyber incidents. It can be purchased as a standalone policy or, in some cases, as an addition to other commercial insurance coverage.
The National Association of Insurance Commissioners (NAIC) notes that cyber policies are highly customized and that traditional commercial property and general liability policies may not cover many cyber risks.
Coverage can generally be divided into first-party coverage and third-party coverage. First-party coverage addresses certain losses directly experienced by the insured business, while third-party coverage generally addresses claims or liabilities arising from an incident affecting other parties.
What Does Cyber Insurance Cover?
Data Breach Response
A cyber policy may cover certain costs associated with investigating and responding to a data breach. Depending on the policy, this can include forensic investigation, legal assistance, notification of affected individuals, and related response services.
Some policies may also cover services such as credit monitoring or identity protection for individuals affected by a covered breach.
Business Interruption
A cyber incident can prevent a company from accessing systems needed to operate. Business interruption coverage may help compensate for certain lost income or additional expenses resulting from a covered cyber event.
The exact trigger, waiting period, coverage period, and applicable limits should be reviewed carefully because business interruption provisions differ between policies.
Cyber Extortion and Ransomware
Some cyber insurance policies provide coverage for expenses associated with cyber extortion or ransomware incidents. Depending on the policy and applicable law, coverage may include certain investigation, negotiation, recovery, or extortion-related expenses.
Ransom payments should not be assumed to be automatically covered. Policies can impose conditions, sublimits, exclusions, and notification requirements. Businesses should understand these provisions before an incident occurs.
Data Recovery
A cyber incident may corrupt, delete, or make business data inaccessible. Certain policies can cover expenses associated with restoring or recovering affected data and systems.
Coverage can depend on the cause of the loss and the policy definition of a covered event.
Cyber Liability
Third-party cyber liability coverage can help address claims brought by customers, business partners, or other parties following a covered cyber incident.
Potential costs may include legal defense, settlements, and certain damages or regulatory-related expenses, subject to the policy terms and applicable law.
Legal and Regulatory Expenses
Data breaches can create legal obligations and regulatory exposure. Some cyber policies provide coverage for legal services, regulatory investigations, and certain expenses associated with responding to privacy or security incidents.
Businesses should examine the specific regulatory coverage provided because not every fine, penalty, investigation, or legal expense will necessarily be covered.
Common Cyber Insurance Exclusions
Cyber insurance does not cover every type of technology-related loss. Common exclusions or limitations can involve:
- Known security vulnerabilities or incidents that existed before the policy began
- Certain acts of war or hostile actions
- Losses outside the policy's defined cyber events
- Certain contractual liabilities
- Intentional or fraudulent acts
- Costs associated with improving systems beyond restoring them
- Certain reputational or intellectual property losses
- Losses exceeding policy limits or applicable sublimits
Policy language varies considerably between insurers. Businesses should review exclusions rather than assuming that a policy covers every consequence of a cyberattack.
Cyber Insurance and Cybersecurity
Cyber insurance is generally intended to complement cybersecurity rather than replace it.
Insurers may ask applicants about security controls such as multifactor authentication, employee training, endpoint protection, backups, access controls, vulnerability management, and incident-response procedures.
Some policies can also contain conditions requiring an organization to maintain particular security measures. A failure to meet policy requirements can potentially affect coverage.
For this reason, businesses should treat cybersecurity practices and insurance coverage as connected parts of a broader risk-management strategy.
How Much Cyber Insurance Does a Business Need?
There is no universal coverage amount that applies to every business. The appropriate limit depends on the organization's potential exposure and financial circumstances.
Businesses can begin by assessing:
Data and Information
Consider the type and volume of information the company stores, including customer information, employee records, payment data, intellectual property, and confidential business information.
Business Dependence on Technology
A company that relies heavily on cloud applications, online transactions, or interconnected systems may experience significant operational disruption if those systems become unavailable.
Revenue and Downtime
Estimate how much revenue the business could lose during different periods of system disruption. Additional expenses required to continue operations should also be considered.
Third-Party Obligations
Contracts with customers, vendors, payment providers, and business partners may impose cybersecurity or notification requirements. These obligations can influence the company's potential exposure.
Existing Insurance
Review property, general liability, professional liability, crime, business interruption, and other existing policies. Understanding where existing coverage begins and ends can help identify potential gaps.
Key Considerations When Choosing Cyber Insurance
Coverage Limits and Sublimits
A policy may have an overall limit as well as separate sublimits for particular types of losses. Businesses should determine whether those limits are sufficient for their expected exposure.
Deductibles and Retentions
Review how much the business must pay before insurance coverage applies. Higher deductibles may affect the company's ability to absorb the initial costs of an incident.
Exclusions
Exclusions can significantly affect the practical value of a policy. Businesses should pay particular attention to exclusions related to ransomware, social engineering, system failures, third-party service providers, prior incidents, and security-control failures.
Incident Response Requirements
Some policies require businesses to notify the insurer promptly after discovering an incident or use approved vendors, lawyers, forensic specialists, or breach-response providers.
Understanding these procedures in advance can help avoid confusion during an emergency.
Social Engineering and Fraud
Phishing and business email compromise can result in fraudulent transfers that may not be treated the same way as other cyber losses. Businesses should specifically determine whether social engineering, funds-transfer fraud, or similar events are covered.
Third-Party and Cloud Providers
A business may experience a cyber incident through a cloud provider, software vendor, payment processor, or other service provider. Review whether the policy addresses incidents involving third parties and contingent business interruption.
Claims and Support Services
Some insurers provide access to breach-response specialists, legal counsel, forensic investigators, crisis-management professionals, and other services following a covered incident.
The availability and conditions of these services can be an important part of evaluating a policy.
Cyber Insurance for Small Businesses
Small businesses can also face significant cyber risks. They may hold customer information, process payments, use cloud services, and depend on a relatively small number of technology systems.
For a small business, the potential financial effect of a major incident can be particularly important when evaluating insurance. However, insurers may require applicants to demonstrate specific cybersecurity controls before providing coverage.
Small businesses should therefore assess their security practices before purchasing a policy. Regular backups, strong authentication, employee security training, access controls, and an incident-response plan can help reduce cyber risk while also supporting the insurance application process.
Final Thoughts
Cyber insurance can help businesses manage certain financial consequences of cyber incidents, including breach response, business interruption, data recovery, liability claims, and other covered expenses.
However, coverage differs substantially between policies. Limits, sublimits, exclusions, deductibles, security requirements, and claims procedures can all affect how a policy responds to an incident.
Businesses should assess their cyber risks, review existing insurance, understand their technology dependencies, and carefully examine policy language before purchasing coverage. Cyber insurance works most effectively as one component of a broader approach that combines insurance, cybersecurity controls, employee awareness, backups, and incident-response planning.
References
- National Association of Insurance Commissioners — Cybersecurity
- Insurance Information Institute — Cyber Insurance: A Key Part of a Robust Business Strategy
- National Association of Insurance Commissioners — Cybersecurity Risk Management
- National Association of Insurance Commissioners — Cyber Insurance Report
- National Association of Insurance Commissioners — Ransomware