

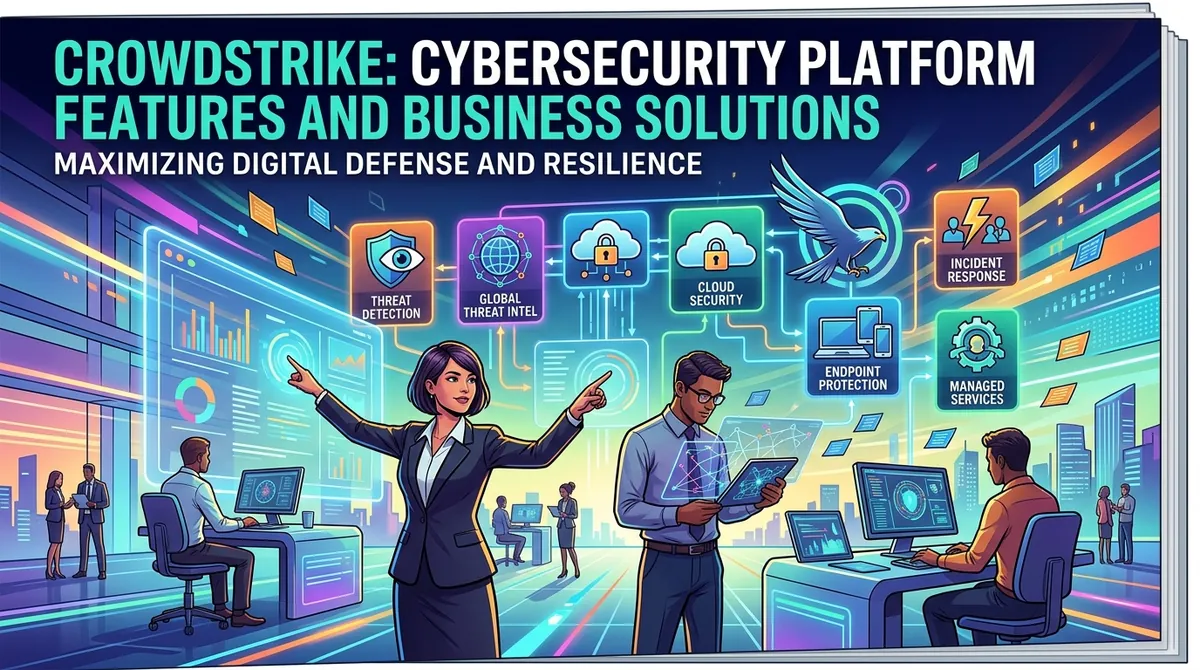
CrowdStrike is a cybersecurity company that provides cloud-native security products through its Falcon platform. The platform is designed to protect endpoints, identities, cloud environments, data, applications, and other parts of an organization's technology infrastructure.
Rather than relying on separate security products for every environment, CrowdStrike combines telemetry and security controls through a unified platform and management console. Its capabilities include endpoint protection, detection and response, threat intelligence, identity security, cloud security, data protection, security operations, and managed services.
CrowdStrike offers packaged Falcon subscriptions for organizations of different sizes as well as additional modules for specialized security requirements. Pricing varies according to the product, device count, deployment, and selected modules.
What Is the CrowdStrike Falcon Platform?
The Falcon platform is CrowdStrike's central cybersecurity environment. It uses a lightweight sensor and cloud-based architecture to collect security information and apply protection across supported environments.
The platform has expanded beyond traditional endpoint antivirus. Current capabilities cover endpoint, identity, cloud, SaaS, data, AI systems, and security operations, allowing security teams to correlate activity across different domains.
This cross-domain approach can provide security teams with additional context when investigating suspicious activity, particularly when an incident involves multiple systems.
Endpoint Security and Protection
Endpoint security remains a core part of Falcon. CrowdStrike provides next-generation antivirus, endpoint detection and response (EDR), device control, firewall management, and mobile protection through different Falcon packages.
The platform is designed to identify malicious activity beyond traditional signature-based malware detection. EDR capabilities provide continuous endpoint visibility and can help security teams investigate suspicious behavior and respond to potential threats.
Device-control capabilities can also be used to manage removable media such as USB and other supported devices.
Threat Detection and Response
Endpoint Detection and Response provides security teams with visibility into activity occurring on protected systems.
Falcon can identify suspicious processes and other behavioral indicators, allowing analysts to investigate activity within a centralized platform. CrowdStrike also provides automated and analyst-assisted response capabilities for containing threats.
Organizations can combine these capabilities with threat intelligence and threat hunting, giving security teams additional information about adversaries and indicators associated with attacks.
Threat Intelligence and Managed Detection
CrowdStrike provides threat intelligence designed to give security teams information about adversaries, attack techniques, and emerging threats.
Organizations that do not maintain large internal security operations teams can also use CrowdStrike's managed services. Falcon Complete provides managed detection and response with expert-led security monitoring, while CrowdStrike also offers specialized threat-hunting services.
Managed services can complement an organization's existing security staff or provide an alternative for businesses that require continuous monitoring without operating a fully staffed security operations center.
Identity Security
Identity has become an important component of modern security because compromised credentials can allow attackers to access otherwise protected systems.
CrowdStrike's Next-Gen Identity Security is designed to protect human, non-human, and AI identities. Capabilities include identity threat detection and response, privileged-access controls, risk-based authentication, and phishing-resistant multifactor authentication.
CrowdStrike also provides FalconID, which uses FIDO2-based authentication and security telemetry to support phishing-resistant access decisions.
Cloud Security
Falcon Cloud Security extends the platform into cloud infrastructure and applications.
Its capabilities include cloud security posture management, cloud detection and response, cloud infrastructure and entitlement management, application security posture management, infrastructure-as-code scanning, and workload protection. Container and Kubernetes security are available through applicable packages.
The platform can correlate cloud activity with endpoint and identity signals, providing security teams with broader context when investigating cloud-related threats.
Data Security
CrowdStrike has expanded its platform into data security, covering sensitive information stored and transferred across endpoints, cloud environments, SaaS applications, browsers, and generative AI tools.
Falcon Data Security can discover and classify sensitive information and monitor how it moves. On endpoints, supported controls can monitor destinations such as websites, removable media, printers, and local applications.
Cloud data security can also identify sensitive information stored in cloud services and monitor potentially risky data movement across APIs, applications, and cloud environments.
AI and Security Operations
CrowdStrike is incorporating AI and agentic capabilities into the Falcon platform.
The platform is designed to help security teams automate investigation and response while maintaining centralized visibility and control. CrowdStrike also provides capabilities for discovering and governing AI agents and monitoring AI-related activity across endpoints, SaaS, and cloud environments.
For security operations teams, these capabilities are intended to reduce the amount of manual investigation required when analyzing large volumes of security events.
Security Operations and SIEM
CrowdStrike provides Next-Gen SIEM capabilities for collecting and analyzing security information across an organization's environment.
SIEM functionality can help security teams bring together security events from multiple sources, search activity, investigate incidents, and support detection and response workflows.
CrowdStrike also provides Falcon Fusion SOAR, which can automate selected security processes and response actions. Its data-security products can integrate with Fusion to route detections and accelerate investigation workflows.
CrowdStrike Falcon Pricing
CrowdStrike publishes several packaged Falcon options for businesses.
Current US pricing includes:
- Falcon Go: $7.99 per device/month, or $59.99 per device/year
- Falcon Pro: $14.99 per device/month, or $99.99 per device/year
- Falcon Enterprise: $19.99 per device/month, or $184.99 per device/year
- Falcon Complete: Contact CrowdStrike for pricing
Falcon Go purchases are currently limited to a maximum of 100 devices. CrowdStrike also offers FalconFlex, which provides access to the broader product portfolio with flexible annual module selection.
Specialized products such as cloud security and additional identity, data, or security-operations modules can use separate pricing models or require a customized quote.
Business Uses for CrowdStrike
Organizations can use CrowdStrike for several security requirements:
- Endpoint and malware protection
- Ransomware detection and response
- Security monitoring
- Threat hunting
- Identity protection
- Cloud security
- Data-loss prevention
- SaaS and AI security
- Security operations
- Managed detection and response
- Compliance and security investigations
The appropriate combination depends on the organization's infrastructure, security team, number of devices, cloud environment, and regulatory requirements.
How Businesses Evaluate CrowdStrike
Organizations generally consider:
- Number and type of endpoints
- Existing security infrastructure
- Internal security-team capabilities
- Identity and access requirements
- Cloud and container workloads
- Sensitive-data requirements
- AI adoption
- Threat-hunting needs
- Managed security requirements
- Security operations and SIEM requirements
- Total licensing and module costs
Businesses should also consider how a security platform integrates with existing identity providers, cloud environments, IT systems, and incident-response processes.
Final Thoughts
CrowdStrike has expanded its Falcon platform from endpoint protection into a broader cybersecurity environment covering endpoints, identity, cloud, data, SaaS, AI, and security operations.
Its offerings range from endpoint-focused Falcon packages to managed detection and response and specialized security modules. The platform's unified architecture allows organizations to correlate information across multiple security domains while maintaining centralized visibility.
For businesses evaluating CrowdStrike, the main considerations include the number of protected devices, existing security capabilities, cloud and identity requirements, data-protection needs, AI adoption, and whether internal teams require additional managed security support.
About the Author
Daniel Brooks, 41, is a business technology consultant at a business advisory publication, specializing in data strategy, operational efficiency, and business intelligence. He helps organizations improve how they manage information and use data to support strategic and operational decisions.